We have been recognized in RegTech100 2026 - Strengthening leadership across AI governance, MRM and FCC

Independent analyst recognition · Chartis 2025
A Category Leader in AI Governance Solutions
Chartis RiskTech Quadrant® for AI Governance Solutions, 2025
Chartis RiskTech Quadrant® for AI Governance Solutions, 2025 — Solytics Partners positioned in the Category Leaders quadrant.
Governance-first DNA
Chartis reserves the Category Leaders quadrant for vendors that pair the highest completeness of offering with the strongest market potential. Four things put us there.
 Governance Engine
 Execution Engine
-
Unified enterprise AI ecosystemTwo platforms — AI Vault and Nimbus Uno — operating as one system.
-
Coverage across every AI assetModels, GenAI applications, RAG systems and autonomous agents.
-
Runtime control for agentsEvery agent action allowed, escalated or blocked before it executes.
-
Evidence generated as work happensAssessments, approvals and controls — audit-ready by default.
Rooted in classic model risk management, Solytics Partners’ AI governance solution offers centralized inventory, risk tiering, workflows, testing and validation across the model lifecycle for traditional, ML and LLM systems.
This was a key factor in its Category Leader placement in our AI Governance quadrant, alongside an ecosystem that offers a model management operating system with governance, validation and continuous monitoring, including templates, telemetry-driven controls and document generators.
Inside the platforms
From governance policy to continuous AI assurance
Four lifecycle actions. Two platforms. One evidence trail from inventory to production monitoring.
AI Vault · Governance engine
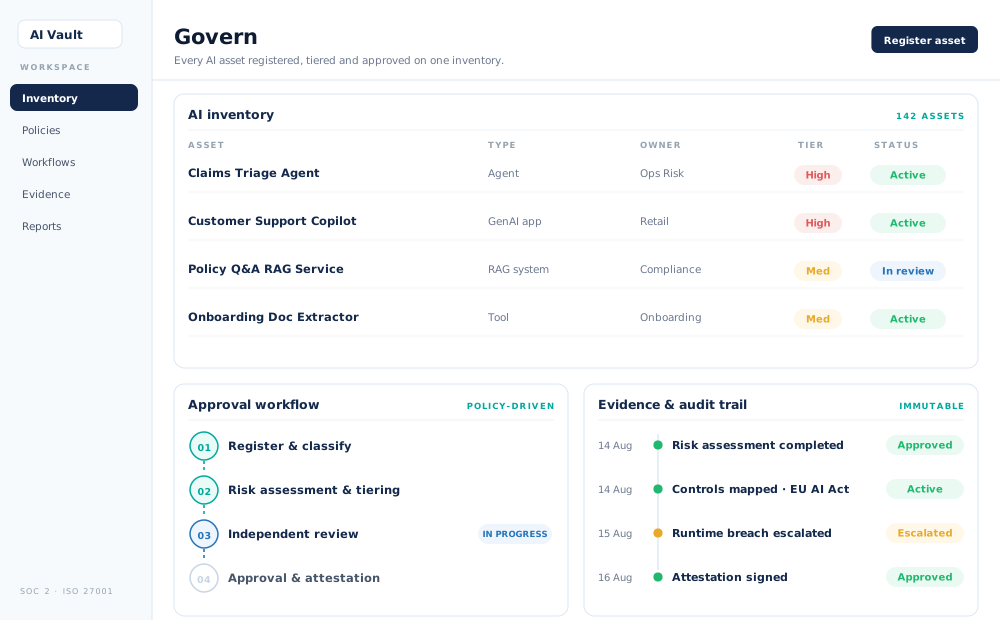
Inventorize every AI asset.
“Know what AI you have and who owns it.”
Every agent, app, RAG service and dataset lands in one inventory — with an owner, a risk tier and a policy set.
- Ownership and lifecycle status
- Risk tiering and materiality
- Audit trail and attestations
Assurance outcome
A tiered inventory with named owners, approval records and an audit trail.
Nimbus Uno · Execution engine
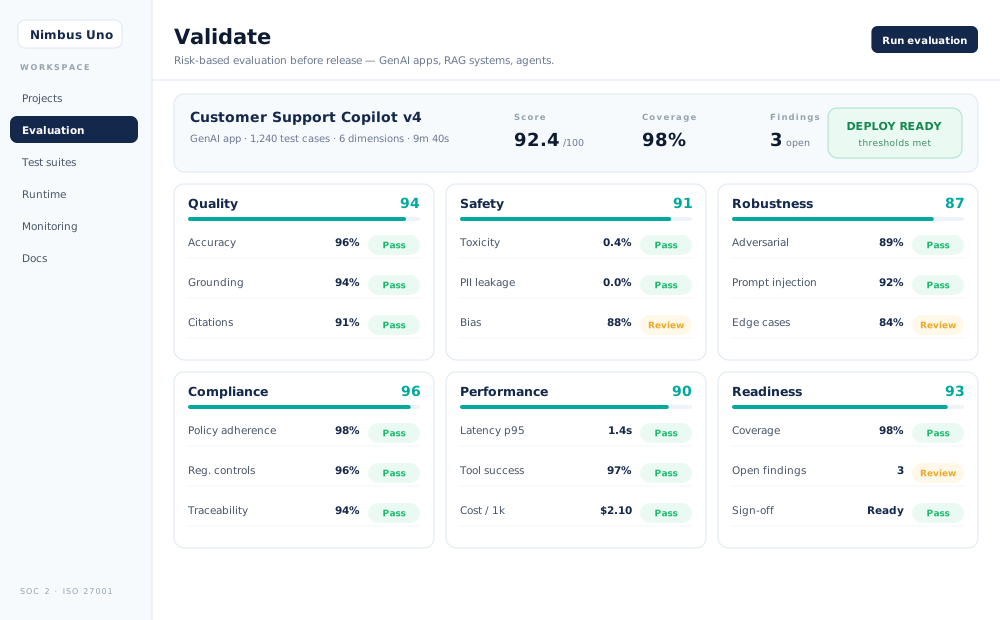
Evaluate every AI system.
“Prove it works before it goes live.”
Test suites score the system against business, policy and safety thresholds before anything is released.
- Quality, safety and robustness
- Adversarial and edge-case testing
- Deployment-ready report
Assurance outcome
A deployment-ready validation report with scores, coverage and open findings.
Nimbus Uno · Assurance Quad
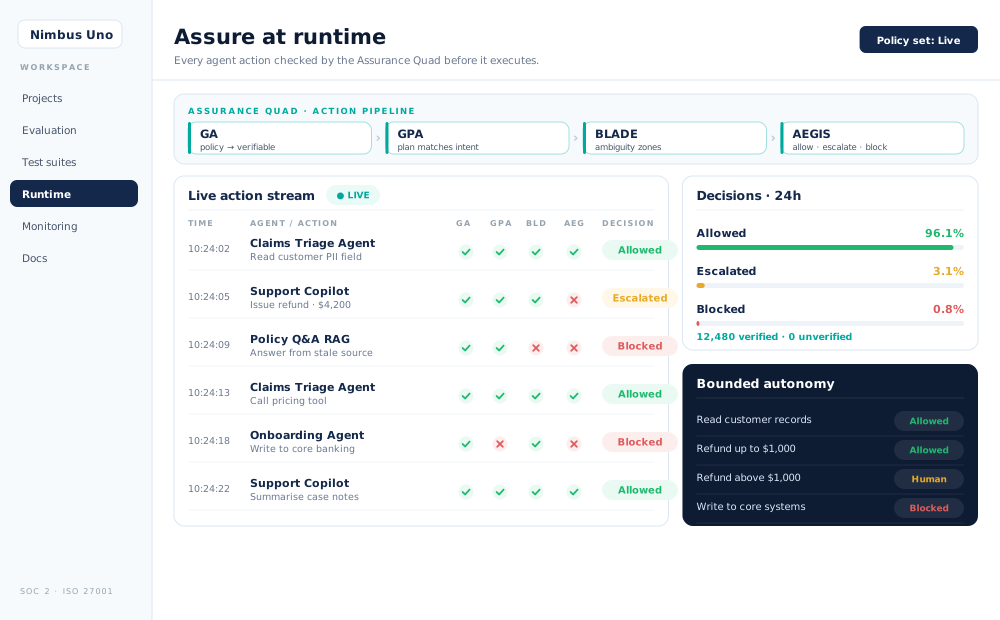
Control every AI action.
“Control what agents are allowed to do.”
Every agent action is checked in the execution path and then allowed, escalated or blocked.
- Policy across plans, tools, permissions
- Autonomy bounded by design
- Step-level audit trail
Assurance outcome
A decision on every action — allowed, escalated or blocked — with a step-level trace.
Nimbus Uno · Execution engine
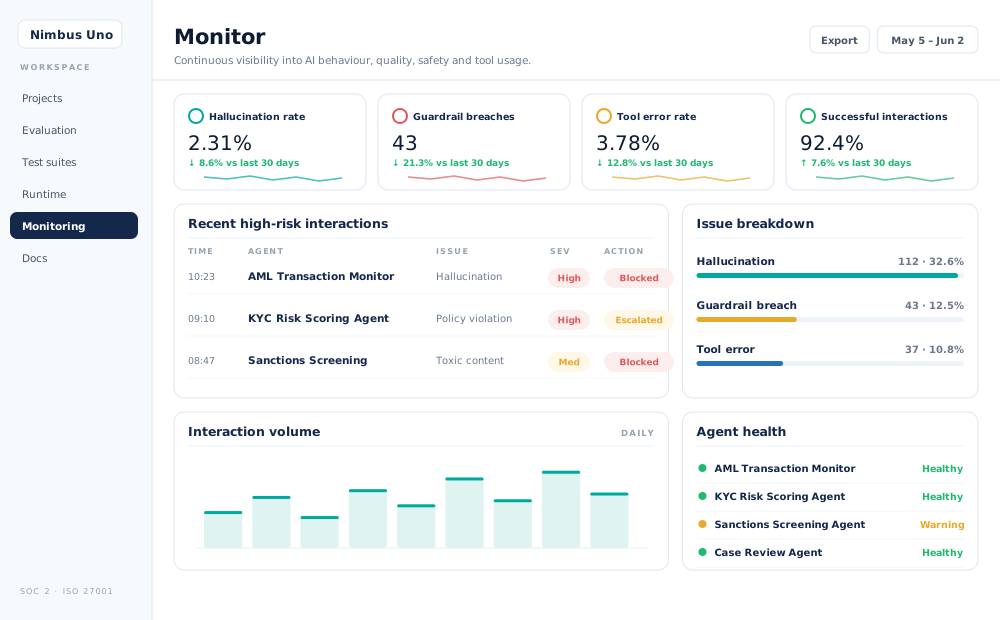
Observe AI in real time.
“See what AI is doing every day.”
Prompts, responses, retrievals and tool calls run through a single monitoring layer.
- 60+ metrics: drift, hallucination, cost
- Real-time alerts and traces
- Agent health at a glance
Assurance outcome
Live dashboards, alerts and traces, with every result written back to the record.
app.solytics-partners.com / ai-governance / inventory
Live
Regulatory Intelligence
Every major AI & model-risk framework. Pre-built and plug-ready.
18+ global AI and model-risk frameworks are mapped to the Solytics ecosystem out of the box — each one tied to the products that operationalize it. No custom rules engineering, no manual mapping.
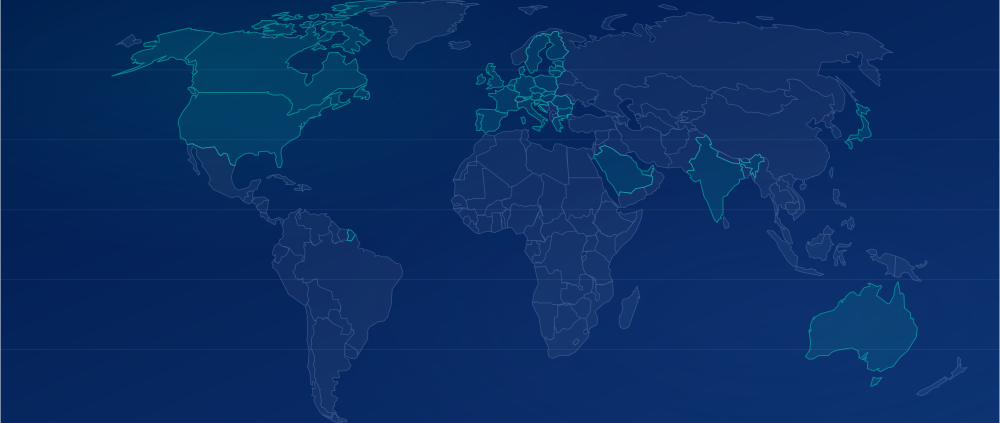
18 frameworks · 6 regions
Hover any marker for detail

Ready to move from AI policy
to continuous proof?

Get complete visibility across models, GenAI applications and autonomous agents — one inventory, one risk tier, one lifecycle.

Enforce policy where it matters — every agent action allowed, escalated or blocked before it executes.

Stay audit-ready by design — evidence mapped to the EU AI Act, NIST AI RMF, ISO 42001, SR 11-7 and local regulation.
Download our AI Assurance brochure
Talk to an expert
Oops! Something went wrong while submitting the form.